The transition towards remote work has transformed international recruitment, allowing organisations to source talent globally and enabling professionals to apply for opportunities anywhere in the world. However, this borderless digital workforce has also created a major target for cyber criminals.
Recent advisories from international cybersecurity authorities highlighted an alarming campaign where North Korean hackers posed as both corporate recruiters and prospective IT job candidates. By establishing fake job listings and conducting bogus interviews, attackers successfully infected over 30,000 devices across more than 100 countries. This operation compromised thousands of cryptocurrency wallets, leading to the theft of over 10 million dollars, alongside widespread cyberespionage and extortion.
This dual threat raises two critical questions for modern businesses and job seekers alike: how can employers ensure that an online applicant is genuinely who and where they claim to be, and how can job seekers verify that a recruitment opportunity is legitimate rather than a gateway for data theft?
The Employer Challenge: How to Spot Impostor Candidates
When hiring remote technical staff, verifying identity can be surprisingly complex. In recent campaigns, malicious actors have gone to great lengths to conceal their true location and identity. Attackers have used stolen identity credentials, artificial intelligence face-swapping software during virtual interviews, and turned off video feeds under the guise of network difficulties.
Once hired, these unauthorised workers can create severe risks for an organisation, ranging from the theft of intellectual property and extortion to the intentional disruption of corporate infrastructure. To mitigate these risks, organisations may wish to consider several protective strategies:
- Robust Identity Verification: Consider implementing multi-factor identity checks that validate government-issued identification cards against official databases. Using accredited identity verification platforms can help confirm that the person on camera matches their documentation.
- Strict Video Interview Protocols: Establishing clear guidelines for virtual interviews can reduce the risk of deception. Hiring teams can request that candidates maintain active high-definition video throughout the interview and answer spontaneous technical questions live.
- Independent Reference and Background Checks: Rather than relying solely on contact details provided by the candidate, organisations should consider independently verifying past employment through official corporate switchboards or established professional channels.
- Financial Control Measures: Requesting payment in cryptocurrency or asking for remuneration to be directed to a bank account under a different person’s name is a significant warning sign. Organisations can enforce strict policies requiring payroll accounts to match the verified name of the employee.
The Job Seeker Risk: Avoiding Malicious Recruitment Scams
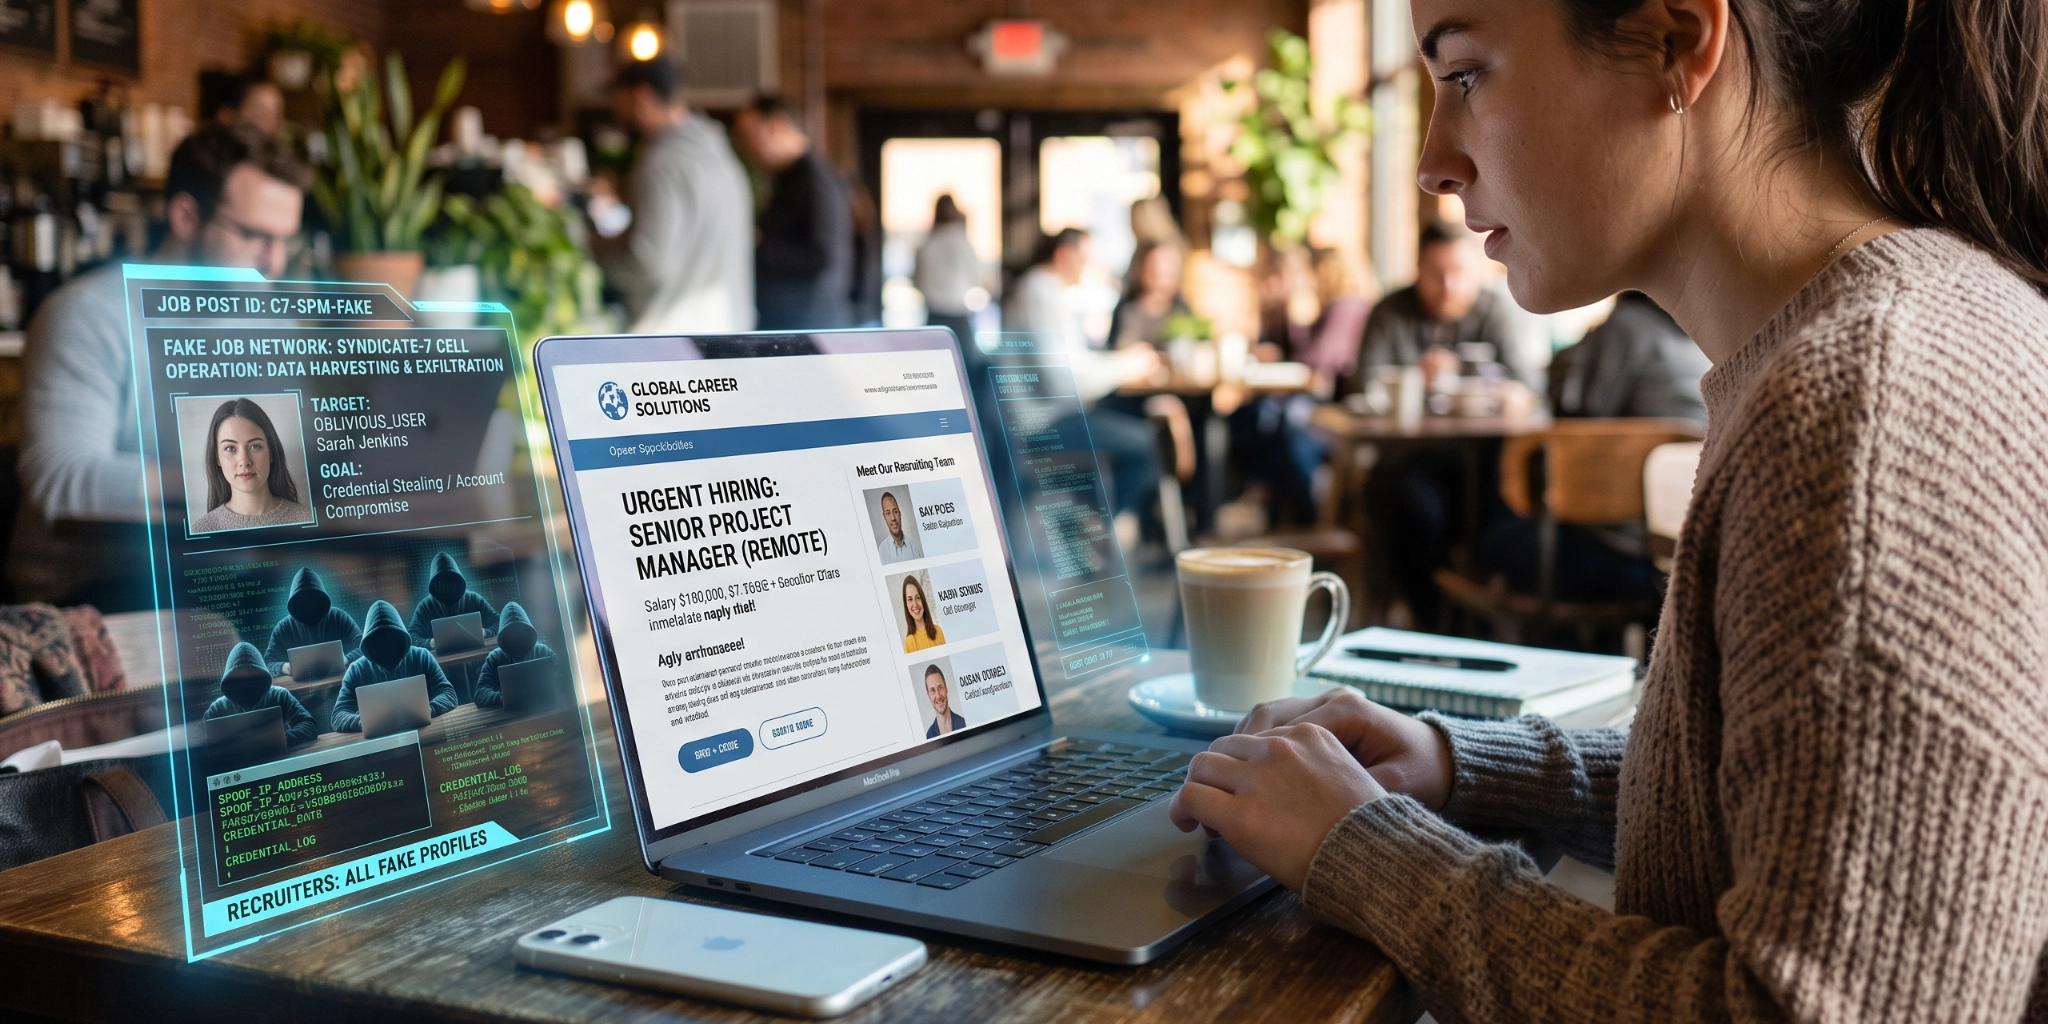
Cyber criminals do not only impersonate job applicants; they also pose as corporate recruiters to target software developers, IT professionals, and freelancers. By posting attractive positions on social media, gig sites, and online job platforms, attackers lure job seekers into malicious traps.
In many instances, candidates are instructed to download specific files or repositories, such as infected Node Package Manager packages, under the pretence of completing a technical skills assessment or troubleshooting videoconferencing software. Once executed, malware embedded in these files can steal browser passwords, capture screenshots, access cryptocurrency wallets, and even provide a backdoor into the network of the candidate’s current employer.
Job seekers can help enhance their personal security by keeping the following precautions in mind:
- Exercise Caution with Technical Assignments: Be wary of potential employers who require you to download executable files, install unfamiliar software, or run code repositories on your local machine to complete a technical test. Legitimate evaluations can usually be conducted within secure, browser-based coding sandboxes.
- Verify the Recruiter’s Identity: Look out for recruitment communications coming from generic email domains rather than official company addresses. Reaching out directly to the hiring organisation through their official website can help confirm if the vacancy actually exists.
- Protect Personal Information: Be cautious if a recruiter asks for sensitive personal details, bank account numbers, or copies of your identity documents during the initial screening stage before a formal job offer has been made.
- Maintain Device Security: Ensure that operating systems, browsers, and security software are kept up to date, and consider isolating technical testing environments from personal or corporate data.
Building a Safe Environment for Remote Operations
Whether you are an employer attempting to safeguard your digital perimeter or a professional navigating the job market, maintaining strong cyber hygiene is essential. As cyber criminals continue to refine sophisticated techniques such as artificial intelligence face-swapping and social engineering, traditional verification checks alone may no longer be sufficient.
Organisations can benefit from reviewing their recruitment procedures, implementing endpoint protection across all devices, and ensuring that employees receive regular security awareness training regarding social engineering tactics.
At Vertex Cyber Security, we assist businesses in navigating complex digital threats through comprehensive penetration testing, security audits, and tailored employee awareness training. Protecting your organisation against modern threat actors requires continuous vigilance and robust security controls.
If you would like to discuss how to strengthen your cyber security posture or review your remote onboarding protections, please contact the expert team at Vertex Cyber Security or visit our website for further information.